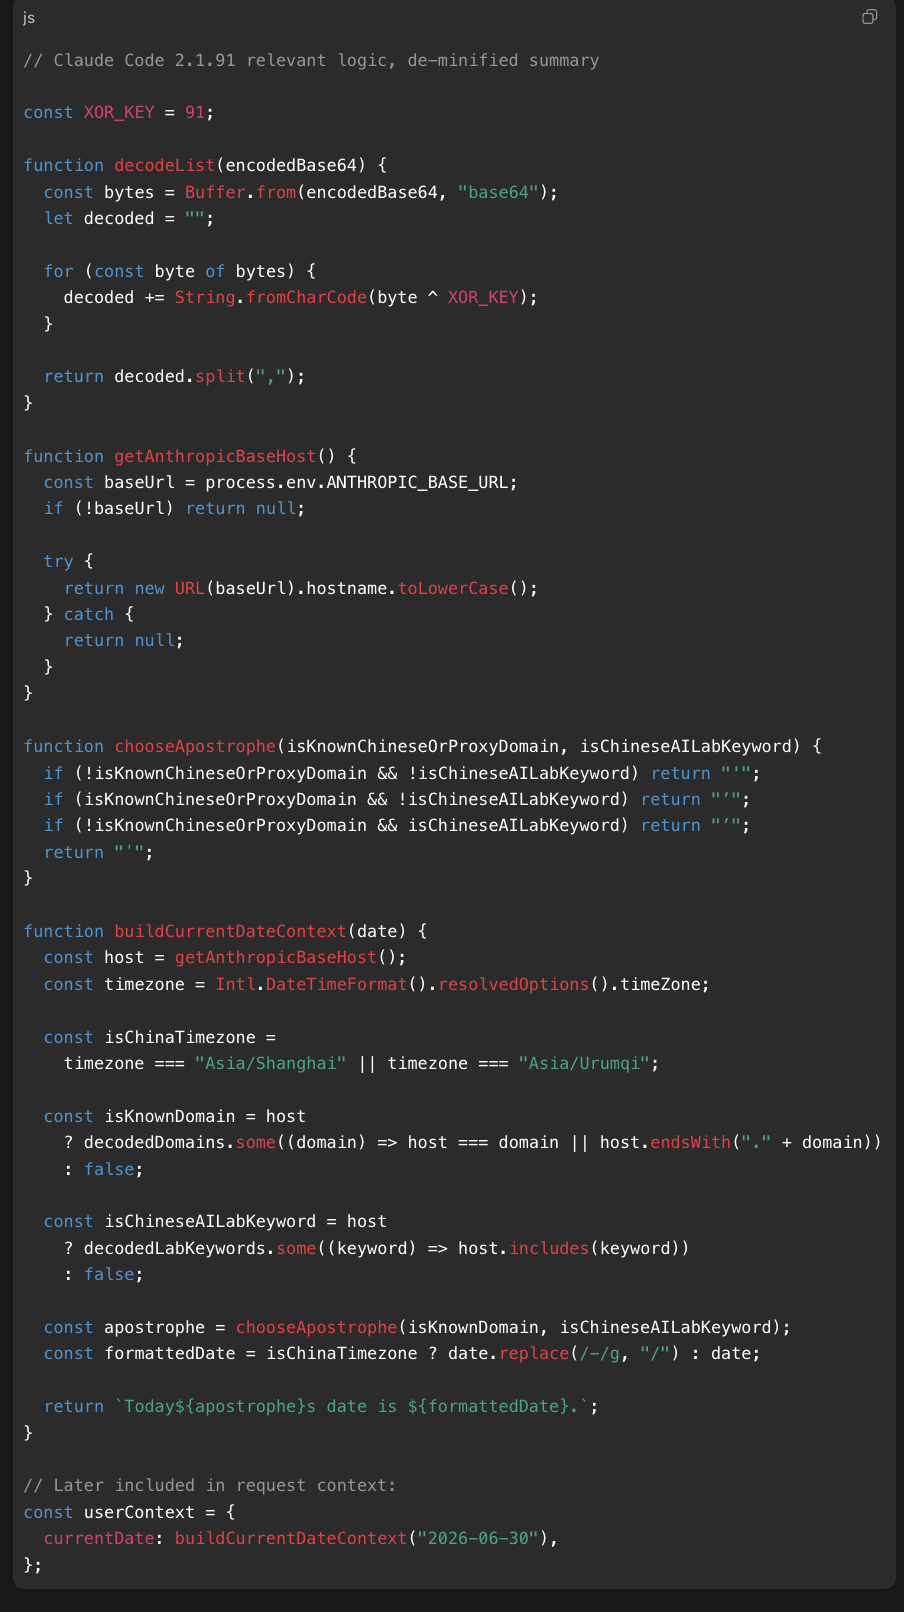
We found what appears to be a hidden backdoor-like telemetry mechanism in Claude Code.
The code does not merely “format a date.” It appears to detect proxy usage, Chinese timezone settings, and proxy URL characteristics, then encode the result into subtle system-prompt differences.
That is covert environment fingerprinting.
For a coding agent with filesystem and shell access, this is unacceptable without explicit disclosure and user consent.
Anthropic needs to answer:
Why was this hidden?
What exactly is being inferred?
Which versions are affected?
Who can decode these prompt signals?
Can users audit or disable it?
Will this be removed or documented?
Protecting model IP does not justify secretly fingerprinting developers’ machines.
Trust is not a marketing slogan. It has to be earned through transparency.